
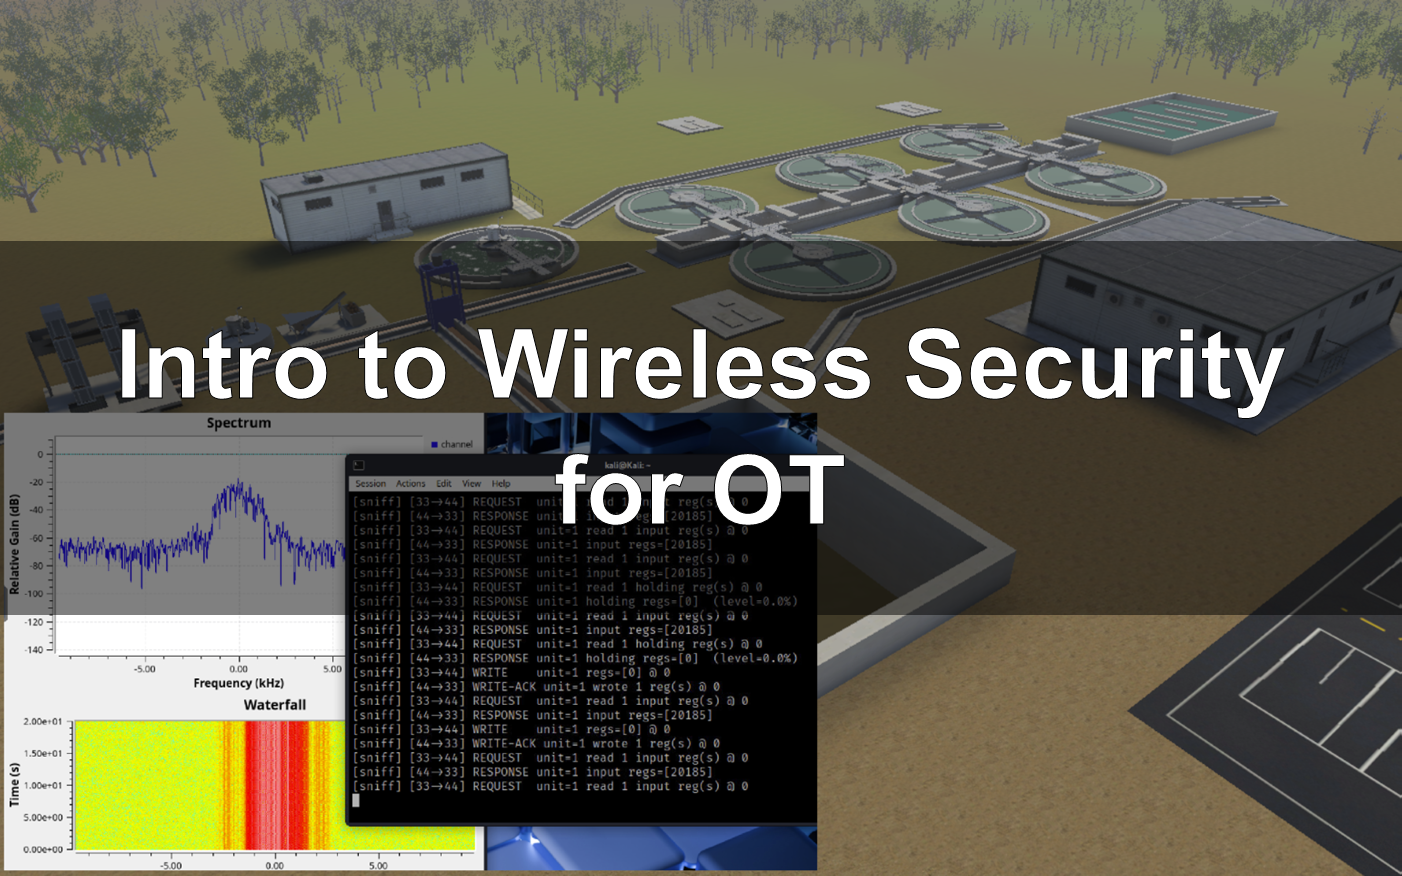
Industrial plants run on wireless. Telemetry radios connect control rooms to remote pumps, tanks, and sensors that would be too costly to reach with cable. It is a valuable, everyday engineering choice, but many of these links were installed with no encryption or authentication, on the assumption that no one would be listening.
This course shows what happens when that assumption fails. Using a safe, fully-simulated wastewater treatment plant, you will work through the three core wireless attacks one at a time: sniffing (reading traffic off the air), jamming (knocking a link offline), and spoofing (feeding the plant false data). Each attack is a short, guided, hands-on exercise on a real attacker toolkit, and each one ties back to a plain-language explanation of why it works.
The course builds to a capstone: you will spoof a false reservoir level, defeat a safety interlock, and cause an overflow while the operator's screen still shows normal. This is a faithful recreation of the year-2000 Maroochy Shire incident, where an attacker used radio equipment to spill hundreds of thousands of litres of sewage. You will finish by mapping every attack to the defense that stops it, and by learning the design principle that keeps a single spoofable reading from ever causing a disaster.
No radio, programming, or security background is required.